I was squeamish about being pwned after my password was continually rejected today in terminal. It worked for mounting drives and gparted. Same time too so not a caps lock things. Eventually it worked after continuous lockouts. **WTF??? [**no I did not start a thread for this but read some old ones].
To the point: eos Cinnamon passed with flying colors: “no malicious software”
Like Lynis it offered 100 suggestions like
If not required, consider explicit disabling of core dump in /etc/security/limits.conf file [KRNL-5820]

Related resources

Article: Understand and configure core dumps on Linux: https://linux-audit.com/software/understand-and-configure-core-dumps-work-on-linux/

Website: https://cisofy.com/lynis/controls/KRNL-5820/
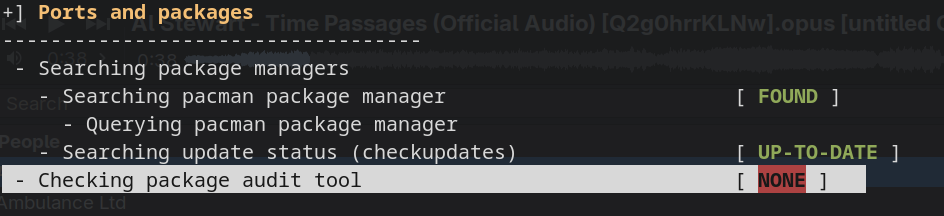
About the package audit tool, it is looking for auditd or equivalent to be installed. That will help to determine which application and which package had done what. Please do note that auditd will create humongous log files inside the directory /var/log/audit. One has to be proficient in understanding the audit log files created by auditd.
It is a good to have. If you are running a server, a definite/mandatory yes. If running a desktop, then yes would be good to have. Recommendation is to have it.
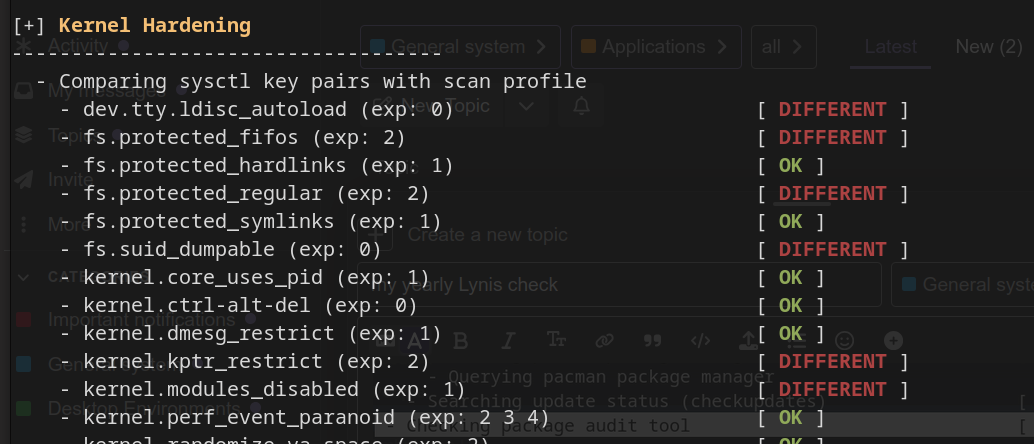
These are kernel hardening parameters. With the expected value, i.e. exp. @drunkenvicar in the lynis log file, typically $HOME/lynis.log or /var/log/lynis.log, what is the value of “Hardening index :” and Hardening strength: that you see?
The package rkhunter in Arch repos point to https://rkhunter.sourceforge.net/ which has not been updated since 2018/19. The github repo for rkhunter has not been updated for the past 9 years. Is rkhunter still relevant and usefull?
I’ve done that a time or too–the understanding part. I like their suggestions. Someday I’ll take them. It’s tempting to want an gov-level hardened machine…I wonder at what cost that comes at? Linux Smarties always preach “assess your attack vector”–well I assessed mine and it’s boring.
2026-06-02 17:55:05 Hardening index : [61] [############ ]
2026-06-02 17:55:05 Hardening strength: System has been hardened, but could use additional hardening
guessing I’m above average but not what they consider optimal (perhaps)
 sober..