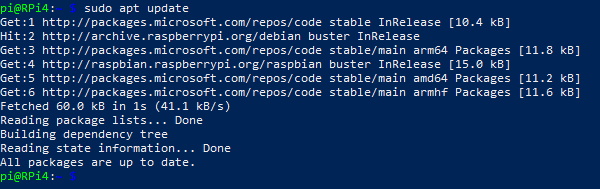
Just saw this topic on the Linux subreddit and thought it might be worth a look for people here that also run Raspberry Pi’s.
Apparently the repo causes any update operation to ping a Microsoft server, essentially allowing them to see that a Raspberry Pi exists at the IP address.
The RPF added a repository to the Raspbian sources list apparently without first informing their users or asking for their permission.
They did this so that installing VS Code would be easier for newbies.
If you have VS Code installed, that repository is going to be accessed for updates.
Microsoft, despite their current stance, has not always been the champion of FOSS (let alone any notion of privacy) that it might have you believe it is today.
Given that, some people might not want any more to do with Microsoft than is necessary - and I’ve purposefully worded it this way so no one could whip out “But Microsoft has contributed to the kernel!!11!1”
Any time you attempt to access a server, such as this repository, the owner of that server can and may see that a connection was attempted from your IP address.
I get to choose what mirrors are used when running pacman - they don’t just magically appear out of thin air unless I don’t check my mirrorlist after updating them.
I was laying this out there for folks to go check their own equipment.
I am turning off my viewing of replies to this topic.
i think the issue is we don’t want microsoft knowing our machines exist. I made mine from parts on amazon so probably everyone knows which ones and how much i spent, including microsoft because they bought that info from amazon at some point
How easy/difficult would it have been for the devs to include a mirror to open source builds of vscode. For eg. in arch we have code package which is the open source build. People specifically wanting MS’ vscode can voluntarily install it from the aur.
I’ve never used an R Pi/Paspbian, so asking for my knowledge: Does the installer ask users if they want to include “non-free repo from a shady company” to their system or does it include the MS repo without any indication whatsoever?
I personally feel that including a repo by MS without “WARNING” the users isn’t not ethical on the dev’s part
Edit: Thanks for informing this. I was planning to set up PiHole sometime later, and I’ll keep an eye out for the vscode repo.
I would say that the reaction is a bit over the top. After all, it is just something they did to make users lives easier IF and only IF they happen to use vscode (which implies some chance of their being aware of the possibilities) and IF and only IF they happen to expose their OWN IP (no VPN for example) and IF and only IF they happen to run the Pi on something other than (for instance) EnOS! Seems fairly lightweight as threats go, especially compared to the things ‘they’ already know (probably including address the Pi was sipped to in the first place!)
Honestly, they could have avoided all of this by making a quick tweet or a blog post about this. Unnecessary drama that just makes the community look bad.
I… don’t see an issue with this. But then some people refuse to use ClearLinux because it is by Intel and Intel are EVIL ™. While using a PC… and arguing you should use Intels products instead of NVIDIA. Because NVIDIA is EVIL ™ but not Intel. Suddenly.
Or refusing to use ANY distro that has ANY connection with a company, be it Fedora, Suse, Ubuntu…
…But then install Steam on their system… And so on.
If you don’t trust any companies or large organizations, why on earth do you live in an apartment, buy food, or use any kind of electronic device. It’s like people yelling about boycotting China while tweeting on their iPhones.